Senior (AI) Platform Engineer & Cloud Architect

Turning cloud complexity
into golden paths.

Azure · AWS · Kubernetes · AI Platforms. I design and scale the cloud infrastructure and developer experience behind mission-critical microservices and next-generation AI platforms — then map it so anyone can understand it.

Currently working across Kubernetes · Terraform · Azure · AWS · GitOps · AI Platforms
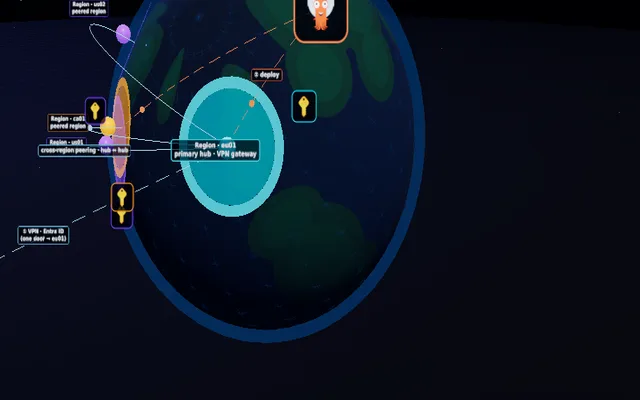
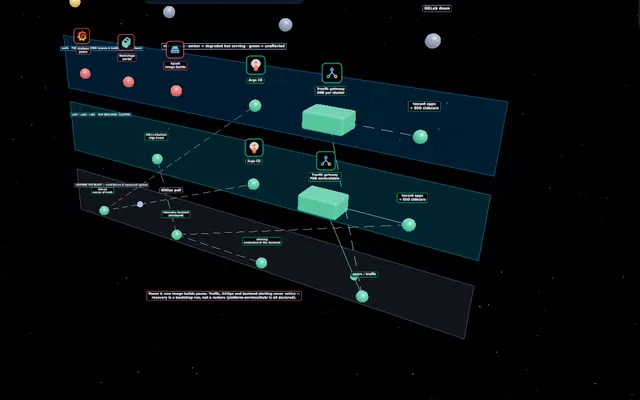
4active regionsmulti-region, one control plane
33platform repositoriesmodules, services, identity, GitOps
4isolated tenantsshared infra, separate blast radius
0standing adminsaccess is code · PIM on activation

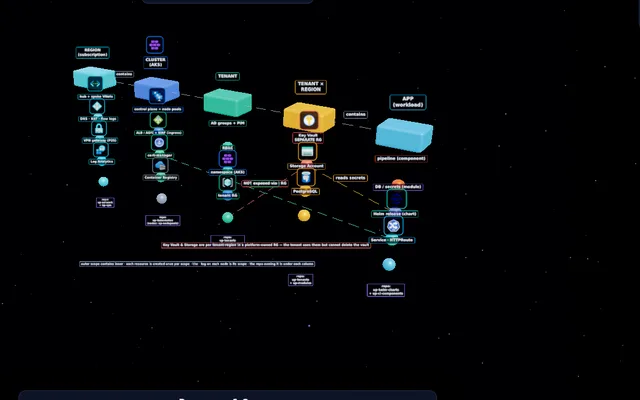
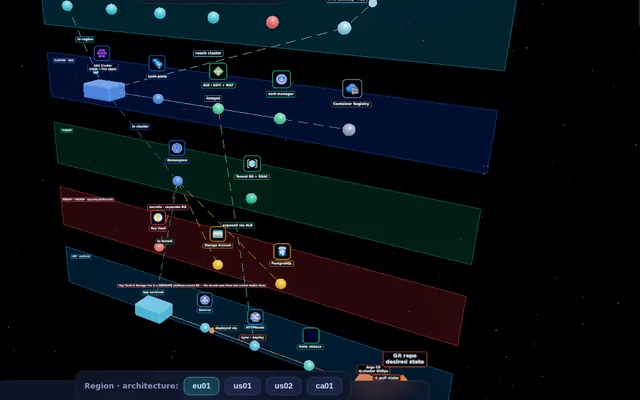
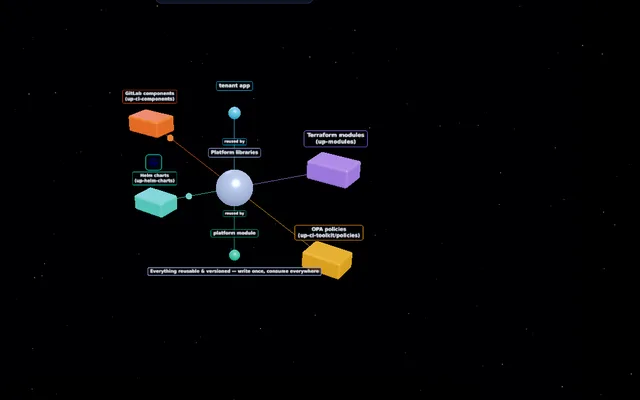
Numbers describe Ultraplatform — the reference platform I model in the 3D map, kept in sync by its live engine. My real-world career impact lives on the CV.

For recruiters — the 10-second versioneverything you need to place me, fast
Role
Senior (AI) Platform Engineer · Cloud Architect
Level
Senior
Availability
Open to new opportunities
Location
Remote (Europe) or on-site · EU / Americas
Core stack
Azure · AWS · AKS/EKS · Terraform · GitOps · OPA
Also
AI platforms · DevEx · FinOps
Experience
15+ years · multi-cloud
Certified
AWS Certified Solutions Architect – Associate · CKA
Languages
Spanish · English
About

Platform engineering at the intersection of
scale and the AI revolution.

I'm a Senior (AI) Platform Engineer and Cloud Architect (AWS Certified Solutions Architect – Associate · CKA) working where large-scale platform engineering meets the AI revolution — designing, scaling and optimizing the cloud infrastructure behind mission-critical microservices and a company's next-generation AI platforms.

My focus is Developer Experience (DevEx): abstracting Azure and AKS so product teams ship safely without being infrastructure experts — golden paths, self-service, policy-as-code guardrails and observability by default.

Over fifteen years I've gone from full-stack product engineering (Klarna, Berlin) to multi-cloud infrastructure (AWS/EKS & Azure/AKS) to designing platforms end-to-end. I care about cost-aware architecture, test-driven infrastructure and making complex systems legible — which is what Ultraplatform, my interactive map, is for.

Off the clock I'm a happy father of three. I love learning, good conversations and weekends in the mountains with my family. My wife is from El Salvador — a country I love for its nature and its people. I value teamwork, and roles where I can help others do their best work.

RoleSenior (AI) Platform Engineer · Cloud Architect
FocusAzure · AWS · AKS · AI Platform · DevEx
CertifiedAWS Certified Solutions Architect – Associate · CKA
Based inCastilla y León, Spain
Experience15+ years
LanguagesSpanish · English
Also buildsDeveloper tooling (OSS-style)
Off the clockFamily, friends and nature
Selected work

Six problems, and the paved roads
that made them stop hurting.

Patterns from the platform I model in the map — each one a problem teams kept hitting, the design that turned it into something self-service, and a link to the proof.

Developer experience

A new service ships through one merge request

Problem
Onboarding a service meant tickets, hand-offs and copy-pasted CI that drifted from every neighbour.
Approach
A golden path: three files in a template wire CI, cloud auth, state isolation and a namespace — all reviewed as an MR.
Result
Teams provision themselves; the guardrails are inherited, not remembered.
Read the write-up
Multi-tenancy

Shared infrastructure, separate blast radius

Problem
Many teams on shared clusters — one team's mistake must never reach another team's data.
Approach
Per-tenant AD groups, resource groups, Key Vaults and namespaces from Terraform; RBAC as the fence.
Result
Multi-tenant efficiency without multi-tenant leakage — isolation you can audit, where a 403 is the design working.
Read the write-up
AI platform

One governed front door to the models

Problem
Every team wanted LLM access, and each was re-solving auth, rate limits and routing on its own.
Approach
An AI gateway that authenticates callers, enforces per-tenant limits and routing, then forwards to the model backend.
Result
A single paved road to AI — governed, observable and per-tenant instead of a scatter of keys.
Open in the 3D map
FinOps

The cost of a change is visible before it merges

Problem
Cloud spend was a monthly surprise — nobody saw the cost of a change until the invoice arrived.
Approach
Infracost prices every Terraform plan in the MR; OpenCost meters the running cluster by tenant and namespace — estimate and reality, side by side.
Result
Cost review moved from a monthly post-mortem to a number in the diff — the same shift-left move the safety gate made for risk.
Read the write-up
Security

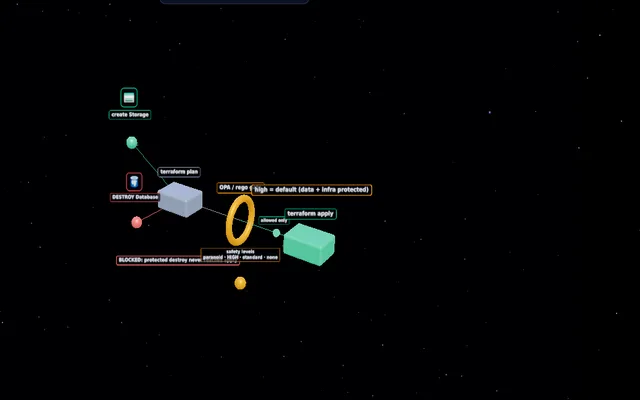
Infrastructure can't change unless policy says it may

Problem
A destructive change (a dropped database, a deleted network) was one wrong terraform apply away, caught only if someone noticed in review.
Approach
An OPA/rego gate evaluates every plan before apply; safety levels block destroys by data sensitivity, composed per cloud provider.
Result
Safety is a wall the change physically cannot pass, not a habit someone might forget — the safe choice is the one you get for free.
Open in the 3D map
Resilience

The scariest failure is rehearsed, not feared

Problem
One shared gateway per cluster is deliberately a shared-fate zone — if it breaks, that's every tenant's outage at once.
Approach
A PodDisruptionBudget floors disruption, and Litmus kills gateway pods on a schedule while a continuous probe proves traffic keeps flowing — the hypothesis and its test, both in code.
Result
"Degraded but serving" is an engineered state, verified monthly — and a clickable failure-mode lens shows what every outage scenario actually takes down.
Open the failure-mode lens
Experience

Fifteen years building & scaling systems.

From full-stack product work to multi-cloud platforms — the throughline is reliability, cost-awareness and developer experience.

~90%cloud cost cut by right-sizing compute (~€1,500/week per env)
15+ yrsfull-stack product → DevOps → platform engineering
2 cloudsAWS/EKS & Azure/AKS migrated and run at scale
TDIbuilt an own Test-Driven Infrastructure framework in Go
Jun 2026 — Present

Senior (AI) Platform Engineer Current

Technosylva · Azure & Kubernetes · AI Platform

Design, scale and optimize the cloud infrastructure powering mission-critical microservices and the company's next-generation AI platforms. Lead Developer Experience: abstracting Azure/AKS complexity behind golden paths, self-service and policy-as-code. Explore the platform I build →

  • AKS at scale — hub-and-spoke networking, tenancy isolation, GitOps delivery
  • Terraform modules, OPA/rego policy gates, secretless CI/CD
  • Foundations for an internal AI platform & AI-assisted developer tooling
↑ Promoted · in Technosylva
Feb 2025 — Jun 2026

Platform Engineer — Azure & Kubernetes

Built and operated the Azure/AKS developer platform: reusable Terraform modules, GitLab CI components, multi-region clusters, and the guardrails that keep tenant teams safe by default.

Apr 2024 — Dec 2024

Software Architect

XERIDIA

Designed clean, maintainable architectures for enterprise applications (incl. OutSystems), focusing on separation of concerns and long-term maintainability.

Oct 2023 — Apr 2024

Masters Director — Business Analytics

Esden Business School

Directed the Business Analytics master's programme — curriculum and mentoring bridging data, analytics and engineering practice.

Oct 2019 — Dec 2023

DevOps — Kubernetes & AWS

SYNAOS · Hannover (Remote)

Migrated infrastructure to AWS (EKS) and Azure (AKS): Packer + Ansible base images, Terraform for the infrastructure, and an own Test-Driven Infrastructure (TDI) framework in Go. Adopted the AWS Well-Architected Framework.

  • Multi-account governance (Control Tower + SSO across Azure/AWS), aws-nuke cleanup
  • Cost-aware design (region/instance/storage/scheduling) — up to 90% savings on instance choices, ~1,500€/week/env
  • Flux & ArgoCD, GitLab Runners on Kubernetes, a DevSecOps pipeline, and always-improving observability
Jan 2017 — Aug 2019

Full-Stack Engineer — Java & React

Klarna · Berlin

Google Pay API integration and a merchant onboarding API (OAuth2). Built an own TDD testing framework; microservices in Java 11 / Spring Boot with React/Redux front-ends, Kafka, and Jenkins CI/CD.

2011 — 2016

Software Engineer — earlier roles

Targetic · Hieronymus · DADA Company · AVANZO

Full-stack PHP/JS (Zend, MySQL, jQuery plugins), database engineering for a social platform, an iOS game (cocos2d / Objective-C), and SCORM e-learning courseware.

Stack

The tools I reach for.

Platform, cloud and delivery — plus the product-engineering background that makes the platform actually usable.

☁️Cloud & Compute

Azure (AKS)AWS (EKS)AWS Certified SA – AssociateCKAKubernetesDockerHelm
↳ see it in the 3D map

🏗️Infrastructure as Code

TerraformPackerAnsibleTest-Driven Infra (Go)
↳ the golden path is three files

🚀Delivery & GitOps

GitLab CIArgoCDFluxJenkinsDevSecOps
↳ run the pipeline before you push it

🛡️Policy & Security

OPA / RegoWell-ArchitectedSSO / PIMSecretless OIDC
↳ defense in depth

🔭Observability

GrafanaLokiMimirDatadogSplunk
↳ SLOs & error budgets

⌨️Languages

GoTypeScript / JSJava · Spring BootPythonPHP
↳ poke around my terminal
Role fit

Hiring for a platform role?
Paste the description.

It runs entirely in your browser — nothing is sent anywhere — and shows which of my core areas your role touches, each with a link to proof.

Private & instant — nothing leaves this page. Ctrl↵ works too.
Landscape

The CNCF landscape I actually run.

Read the notes

Not a logo wall — every tool here runs in the platform today and has an article explaining the job it does and what I'd tell you before adopting it.

⛵ Helm

The packaging grammar — one chart library, consumed everywhere.

Read →

🐙 Argo CD

GitOps delivery — the cluster state is a repo, not a memory.

Read →

🛡️ Kyverno

In-cluster policy: validate, mutate, generate — safe namespaces by default.

Read →

🔑 External Secrets

Key Vault → Kubernetes secrets, without humans in the loop.

Read →

🔄 Reloader

Config and secret changes actually reach running pods.

Read →

🌐 External DNS

DNS records follow the ingresses that need them.

Read →

📈 KEDA

Scale on real signals — queues and events, including to zero.

Read →

🔭 OpenTelemetry

One instrumentation standard every tenant inherits.

Read →

🔌 Telepresence

Debug against the real cluster from the laptop.

Read →

⚡ Karpenter

Just-in-time, right-sized nodes — provisioned in seconds, consolidated when idle.

Read →

📊 Grafana

Dashboards, alerts and Explore as code — one pane over Mimir & Loki.

Read →

🎭 Backstage

The developer portal — software catalog, golden-path scaffolder and TechDocs.

Read →

📦 Buildpacks

Images without Dockerfiles — one hardened builder, no per-repo drift.

Read →

📜 cert-manager

Certificates as a controller — TLS issued and renewed automatically.

Read →

🛡️ Trivy

Continuous vulnerability scanning — CVEs found after deploy, not just at build.

Read →

📋 Policy Reporter

One dashboard for every policy engine's reports — Kyverno and Trivy in one pane.

Read →

💰 OpenCost

Cost allocation per tenant and namespace — the bill made visible.

Read →

⚖️ OPA / rego

Infrastructure can't change unless policy says it may — a plan-time safety gate.

Read →

🦅 Falco

Runtime security — catching what admission policy and image scans can't see.

Read →

🧪 Litmus

Chaos as a reviewed experiment — never ambient, always opt-in.

Read →

🚩 OpenFeature

Decouple the deploy from the release — vendor-neutral feature flags.

Read →

🐝 Cilium

The eBPF CNI, chosen at cluster creation — L3-L7 policy and Hubble visibility.

Read →

🧩 Dapr

Sidecar building blocks — pub/sub, state, durable workflow, one API.

Read →

🚦 Traefik

One shared gateway, many tenant routes — SSO by sidecar, not by app code.

Read →
Tools I build

Developer tooling, local-first.

Try my terminal live

The infrastructure I run isn't the only thing I build — I write the tools that make the day-to-day loop fast and safe.

Daily drivers — not mine, just essential: kindskaffoldtelepresence k9ssterndive gitlab-ci-local

⌨️ Own Neovim and IDE plugins

Grafana Alloy configures with River — I built its missing editor experience end to end.

🤝 Open-source contributions

Everything, tagged → Notes ↗

Francisco Roa
Contact

Let's build something reliable.

Open to conversations about platform engineering, AI platforms, and developer experience.

Open to new opportunities · remote or on-site · Europe, North & Latin America